Resource Center
Welcome to our cybersecurity resource center where we uncover how malicious actors exploit weaknesses in systems, while going beyond the technical aspects and examining real-world perspectives across various industries.
LATEST VULNERABILITIES
CVE-2026-104935 is an actively exploited Ivanti Connect Secure authentication bypass that can enable remote code execution. Review the exploit chain, affected versions, fixed releases, indicators of compromise, and how NodeZero Rapid Response helps validate exposure and verify remediation.
Read More →Attackers are chaining CVE-2026-105133 and CVE-2026-105134 to bypass authentication and achieve remote code execution in AhsayCBS. Explore the technical findings, indicators of compromise, affected versions, hotfixes, and how NodeZero Rapid Response helps validate exposure.
Read More →WEBINAR REPLAY

SEARCH
CATEGORIES
TAGS
SEARCH
CATEGORIES
TAGS
CVE-2026-106173 Deep-Dive: FortiSIEM gRPC Path Traversal File Write RCE
October 20, 2026
Horizon3 researchers analyze CVE-2026-106173, a critical Fortinet FortiSIEM vulnerability affecting an unauthenticated gRPC service. The deep-dive explains how path traversal and null-byte handling enable arbitrary file writes and remote code execution, along with indicators of compromise for defenders.

Cybersecurity Assumptions Graveyard
How AI is raising the need for a new exposure management operating model AI has turned yesterday’s cybersecurity assumptions into ghosts—and attackers are moving at machine speed. Join us to uncover the hidden exposures haunting your environment and learn how a new exposure management operating model can help banish alert overload and build cyber resilience.
From Assumptions to Evidence: Why Validation Is the Heart of CTEM
In this webinar, we'll explore why validation has become one of the most important phases of CTEM, how organizations can move from assumptions to evidence, and why proof is often the difference between debating a finding and taking action.
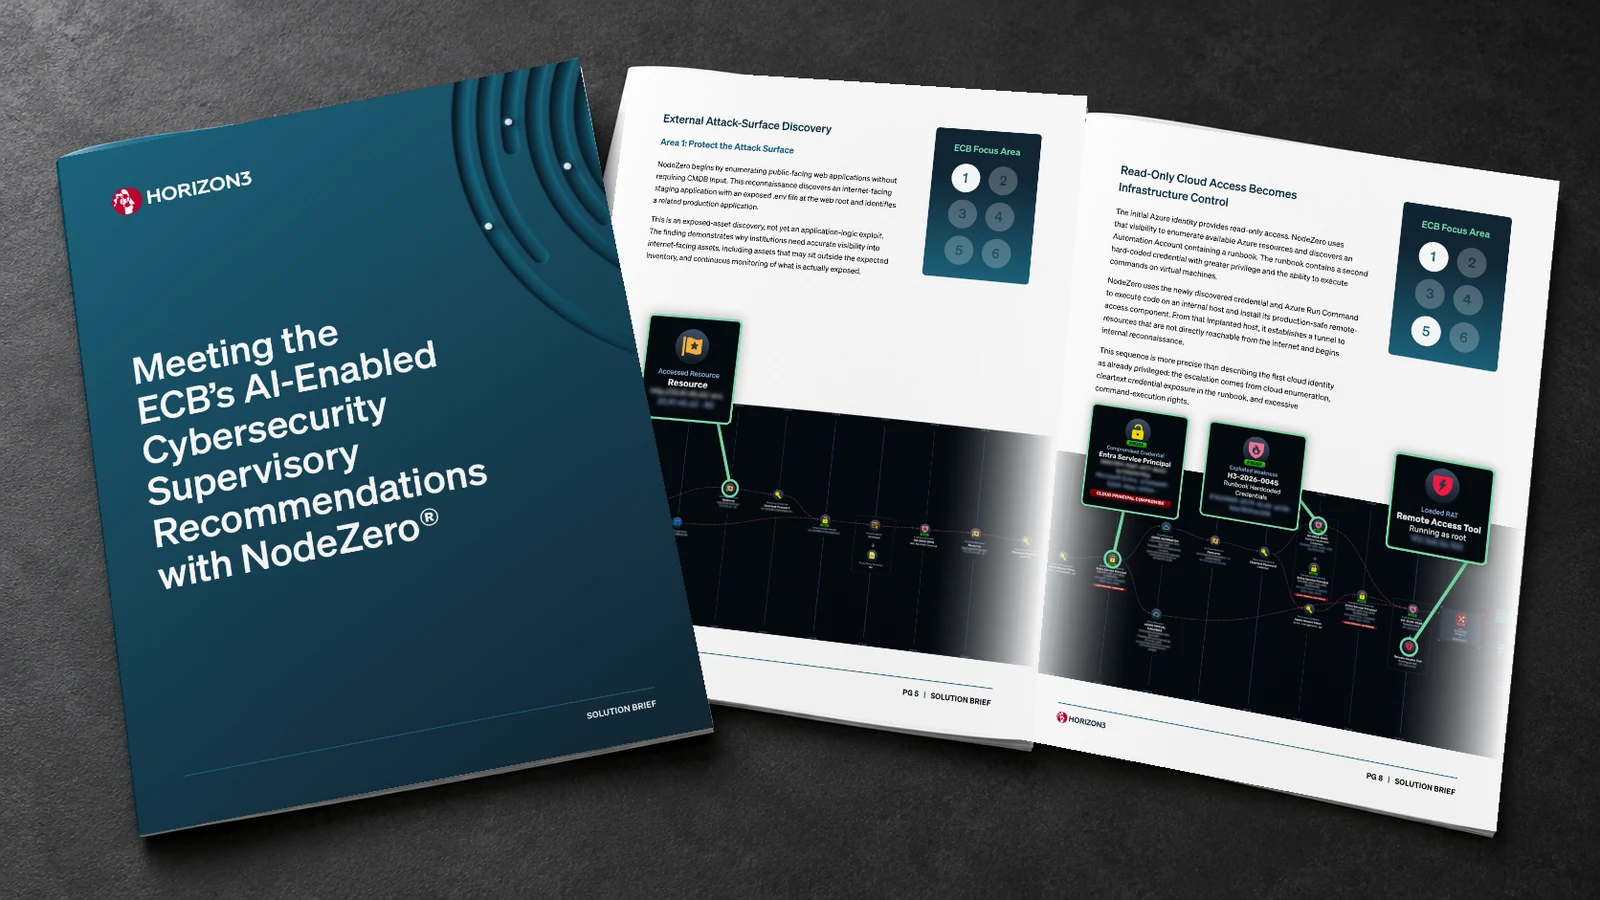
Meeting the ECB’s AI-Enabled Cybersecurity Supervisory Recommendations with NodeZero®
October 16, 2026
Explore how NodeZero autonomous penetration testing connects application, cloud, identity, and infrastructure weaknesses into validated attack paths, helping banks prioritize remediation and build evidence for the ECB’s cybersecurity supervisory recommendations.
CVE-2026-104935
October 15, 2026
CVE-2026-104935 is an actively exploited Ivanti Connect Secure authentication bypass that can enable remote code execution. Review the exploit chain, affected versions, fixed releases, indicators of compromise, and how NodeZero Rapid Response helps validate exposure and verify remediation.
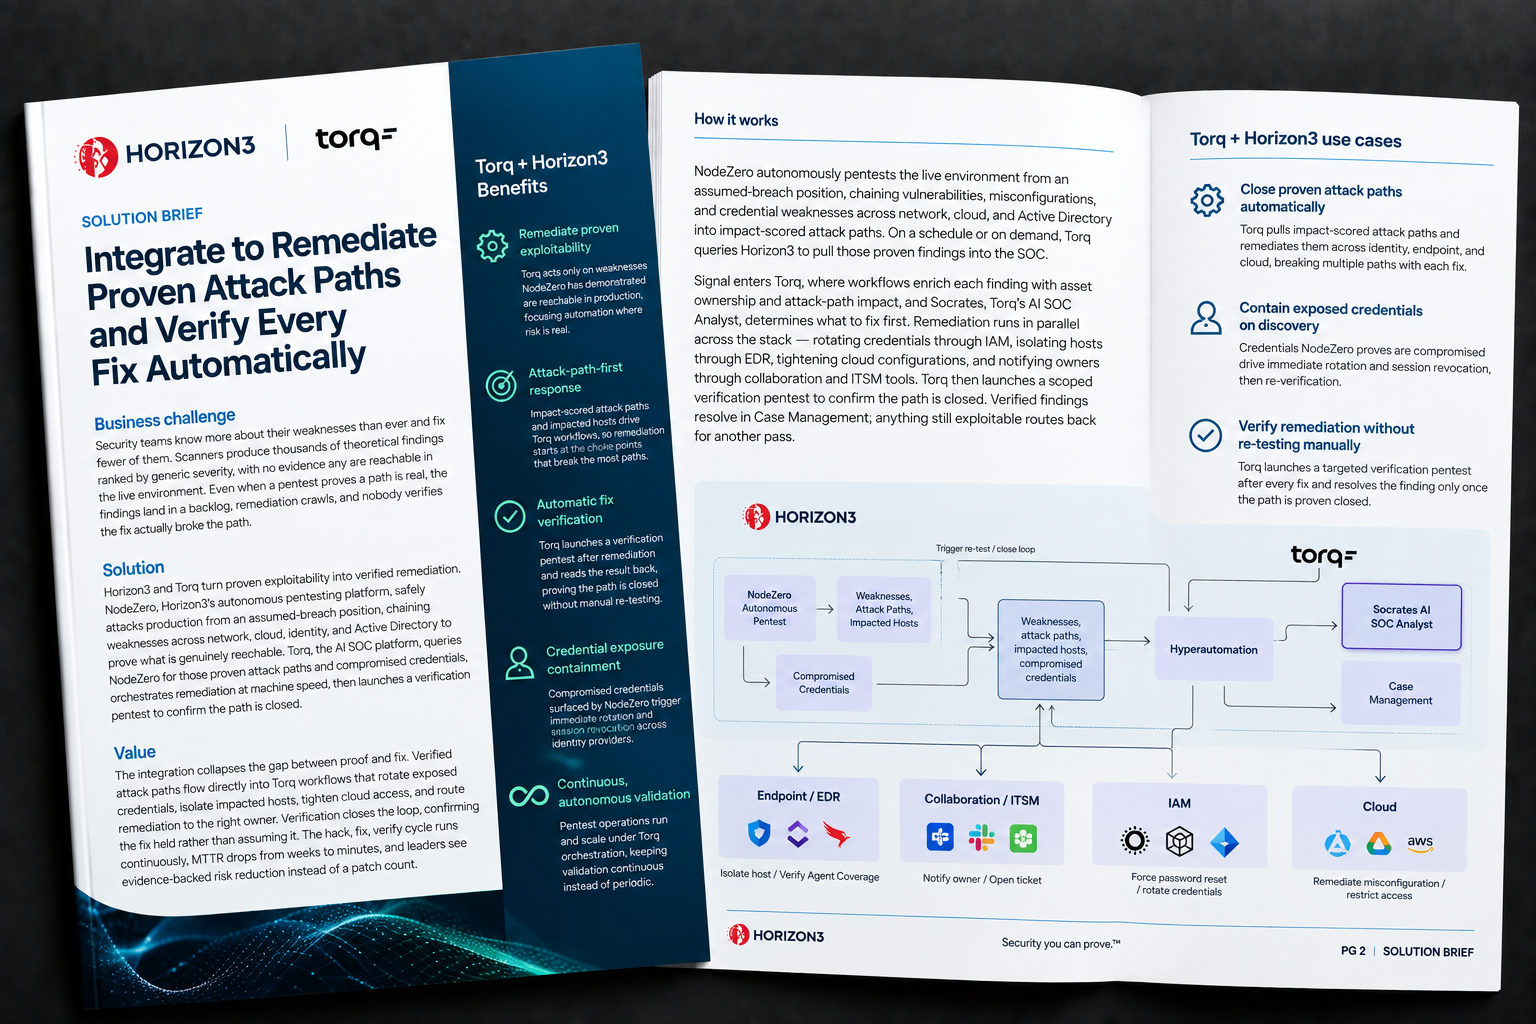
From Proven Attack Paths to Verified Fixes: Horizon3 and Torq Close the Remediation Loop
October 15, 2026
Horizon3 and Torq connect real-world attack-path evidence to security operations, coordinated remediation, and verification. Discover how NodeZero and Torq help teams prioritize exploitable exposures, automate remediation workflows, and confirm that security fixes hold.
CVE-2026-105133 and CVE-2026-105134
October 14, 2026
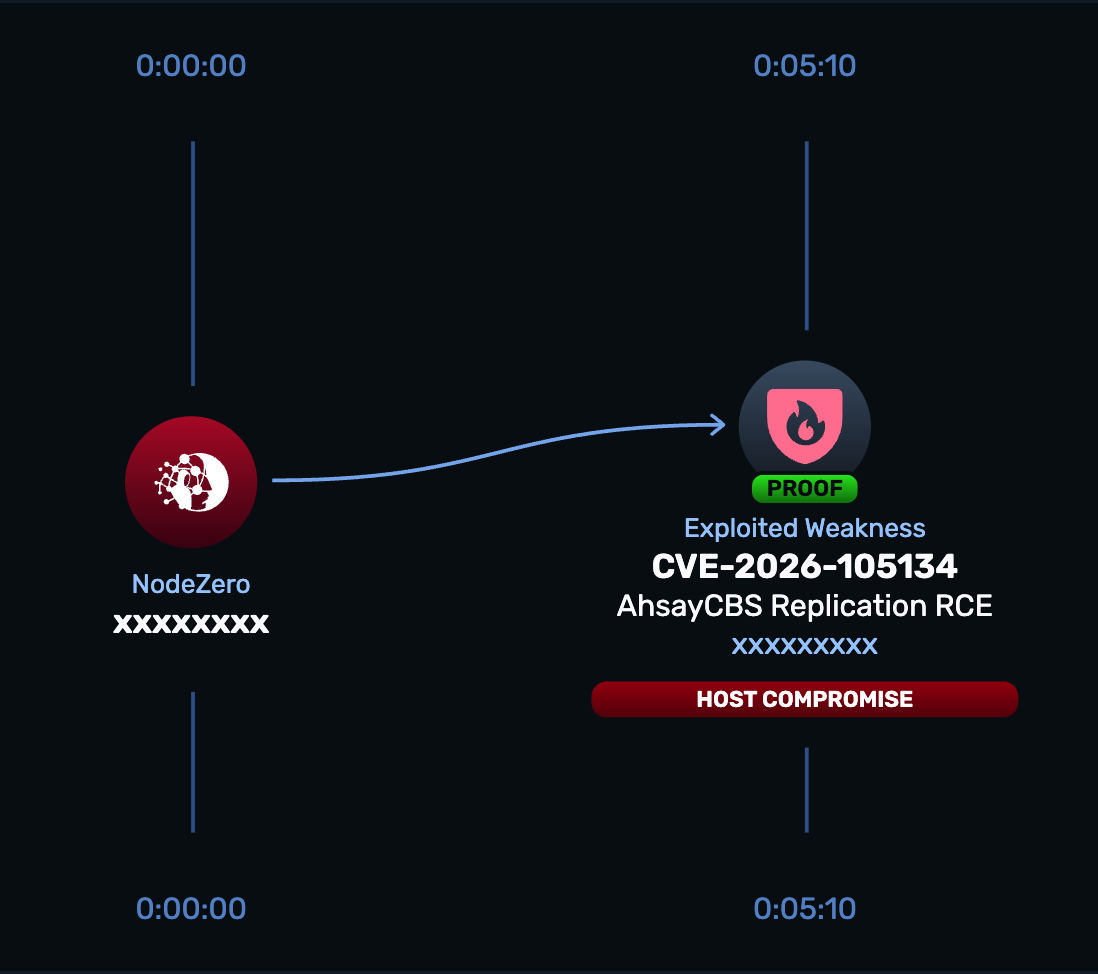
Attackers are chaining CVE-2026-105133 and CVE-2026-105134 to bypass authentication and achieve remote code execution in AhsayCBS. Explore the technical findings, indicators of compromise, affected versions, hotfixes, and how NodeZero Rapid Response helps validate exposure.
AhsayCBS Deep-Dive: Auth Bypass to RCE
October 14, 2026
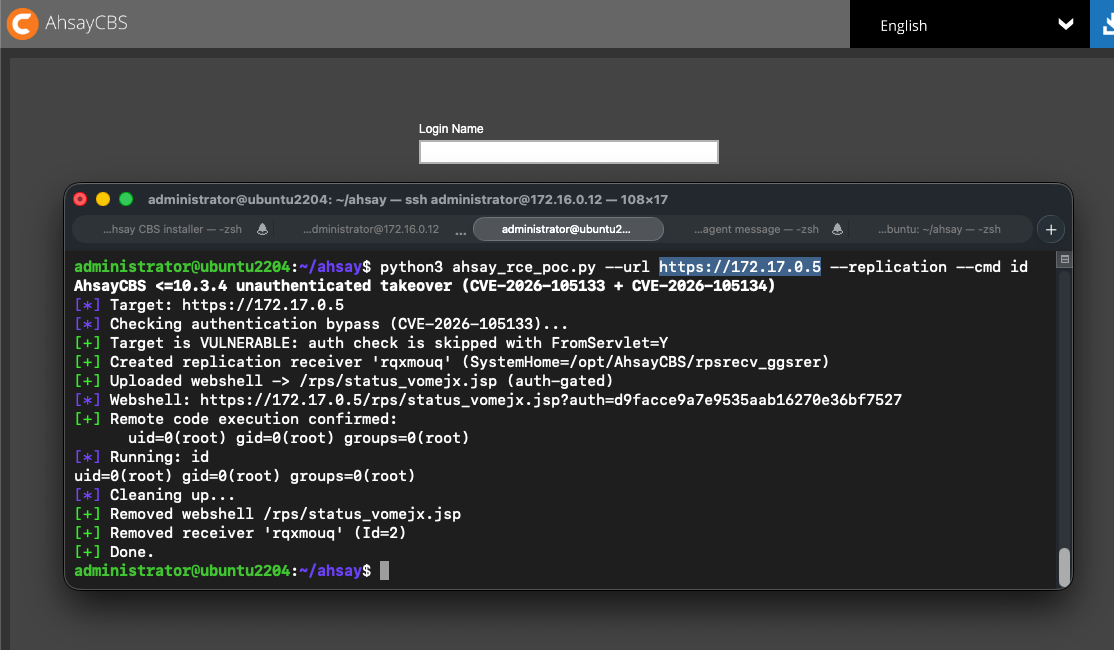
Horizon3 researchers reverse engineer CVE-2026-105133 and CVE-2026-105134 in AhsayCBS, demonstrating how an authentication bypass and path traversal can be chained to create administrator accounts, upload JSP webshells, and achieve remote code execution.
Integrate to Remediate Proven Attack Paths and Verify Every Fix Automatically
Discover how Horizon3 and Torq bring NodeZero® exploitability findings into SOC workflows to orchestrate remediation, contain exposed credentials, and verify that attack paths are closed.
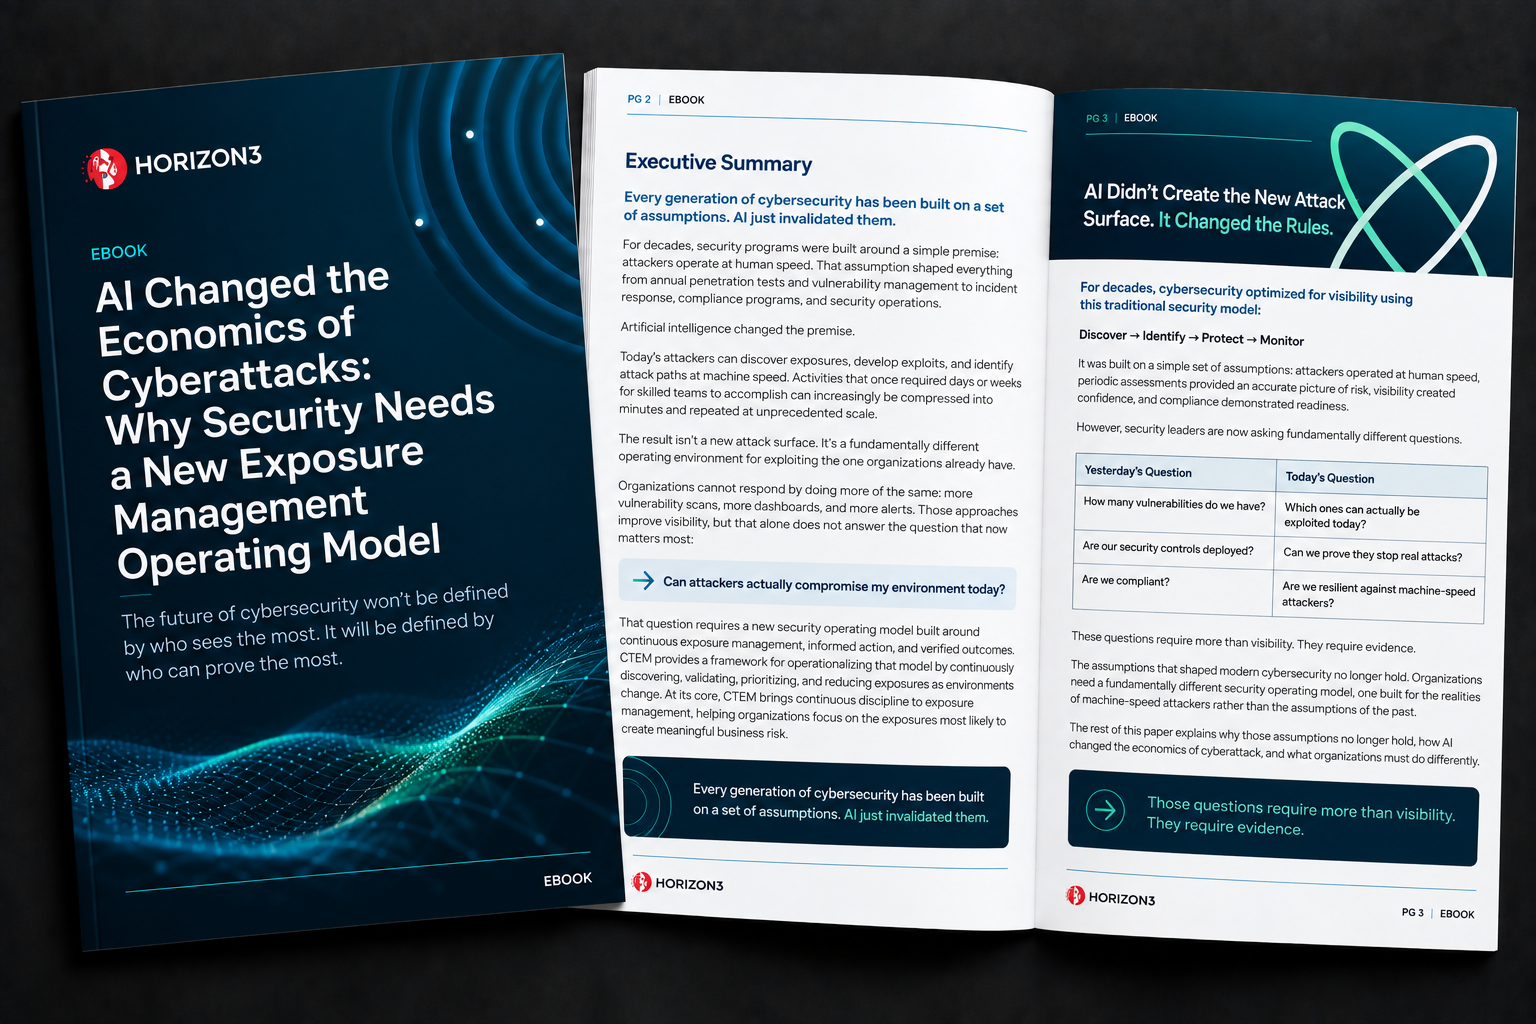
AI Changed the Economics of Cyberattacks
October 9, 2026
AI has changed the speed, scale, and economics of cyberattacks. Learn why modern security requires continuous exposure management built around evidence, informed action, and verified outcomes.